Users & Roles
"Users & Roles" is designed for cluster administrators to manage the organization structure, user accounts, and cluster-level role permissions for the current cluster.
Entry path: Left sidebar menu Cluster Management > Users & Roles, page route
/admin/org.
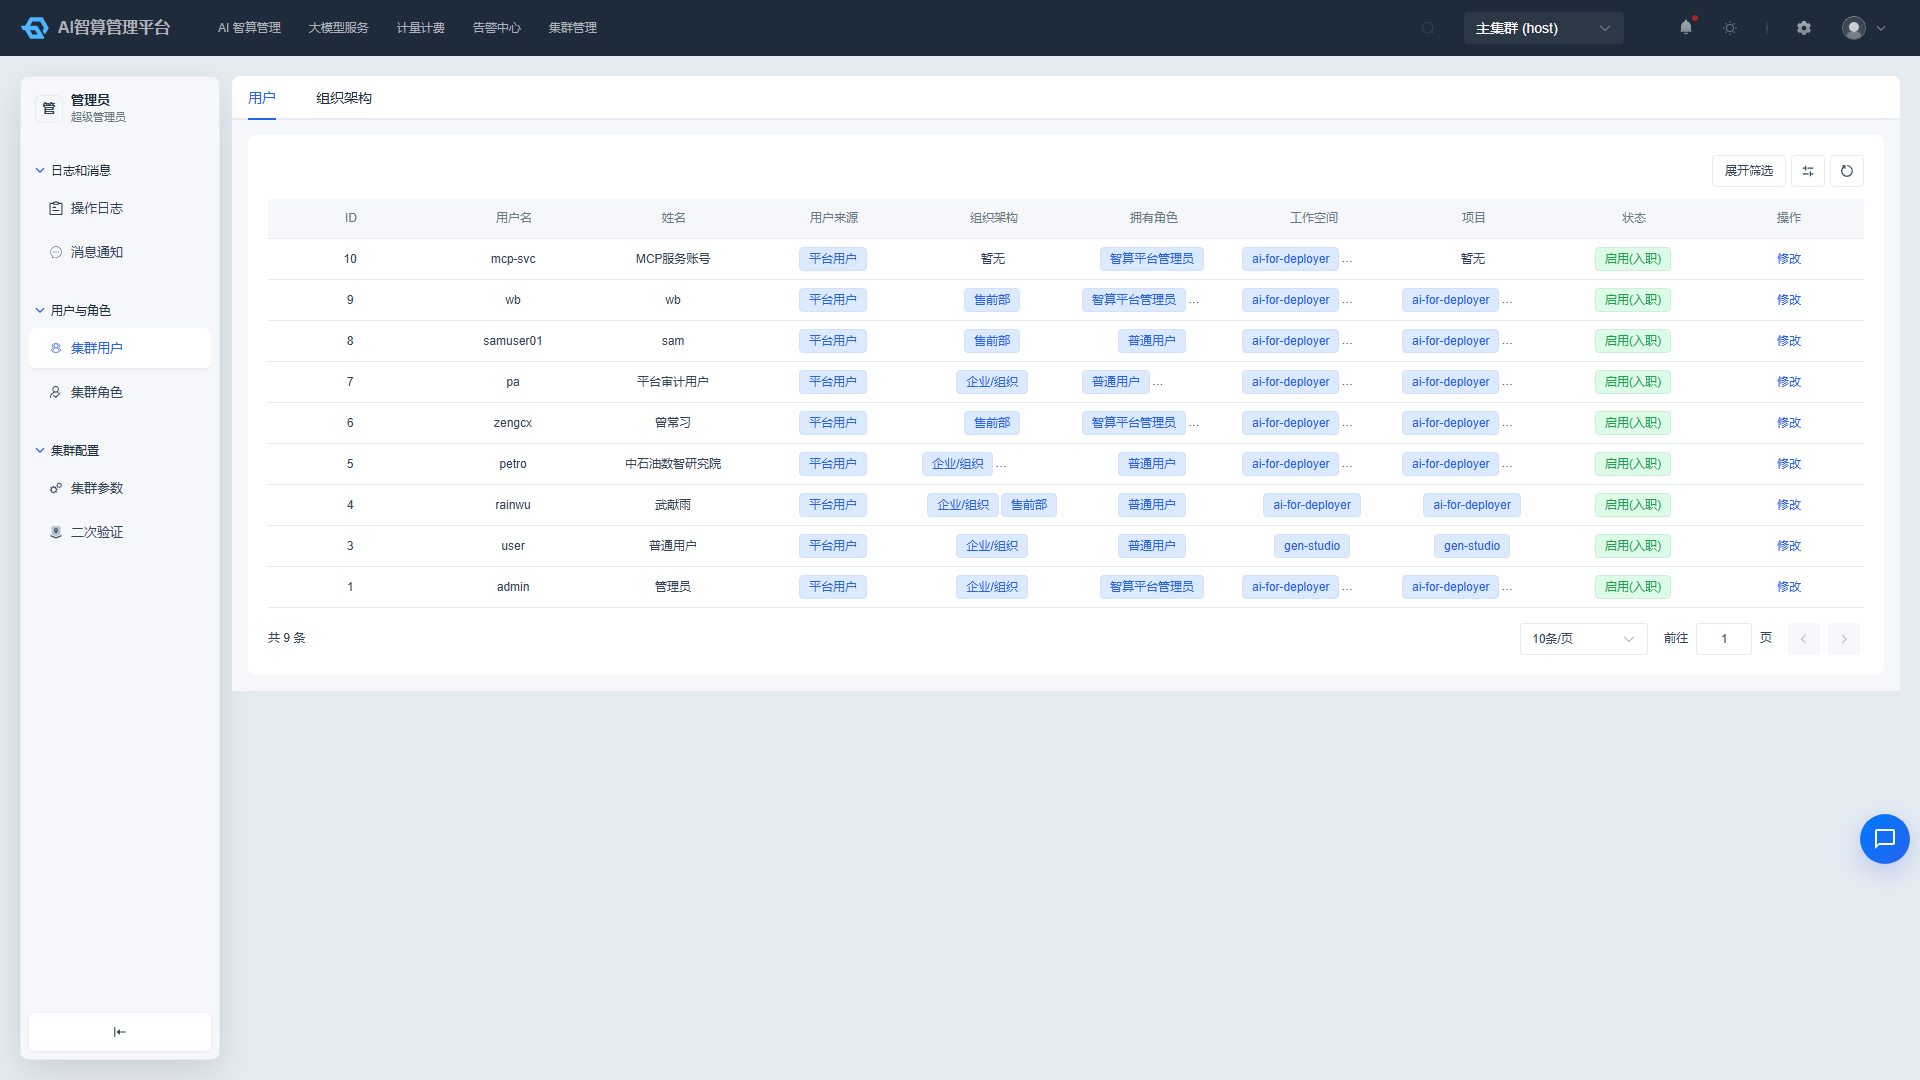
Page Menu
| Page | Route | Description |
|---|---|---|
| Cluster Users | /admin/org/dept | Cluster users and department management |
| Cluster Roles | /admin/org/rbac | Cluster roles and permission management |
| Role Permissions | /admin/org/rbac/permission/:roleUUID | Assign menu/API permissions to roles |
Cluster Users
View Organization Structure
- Navigate to Cluster Management > Users & Roles > Cluster Users.
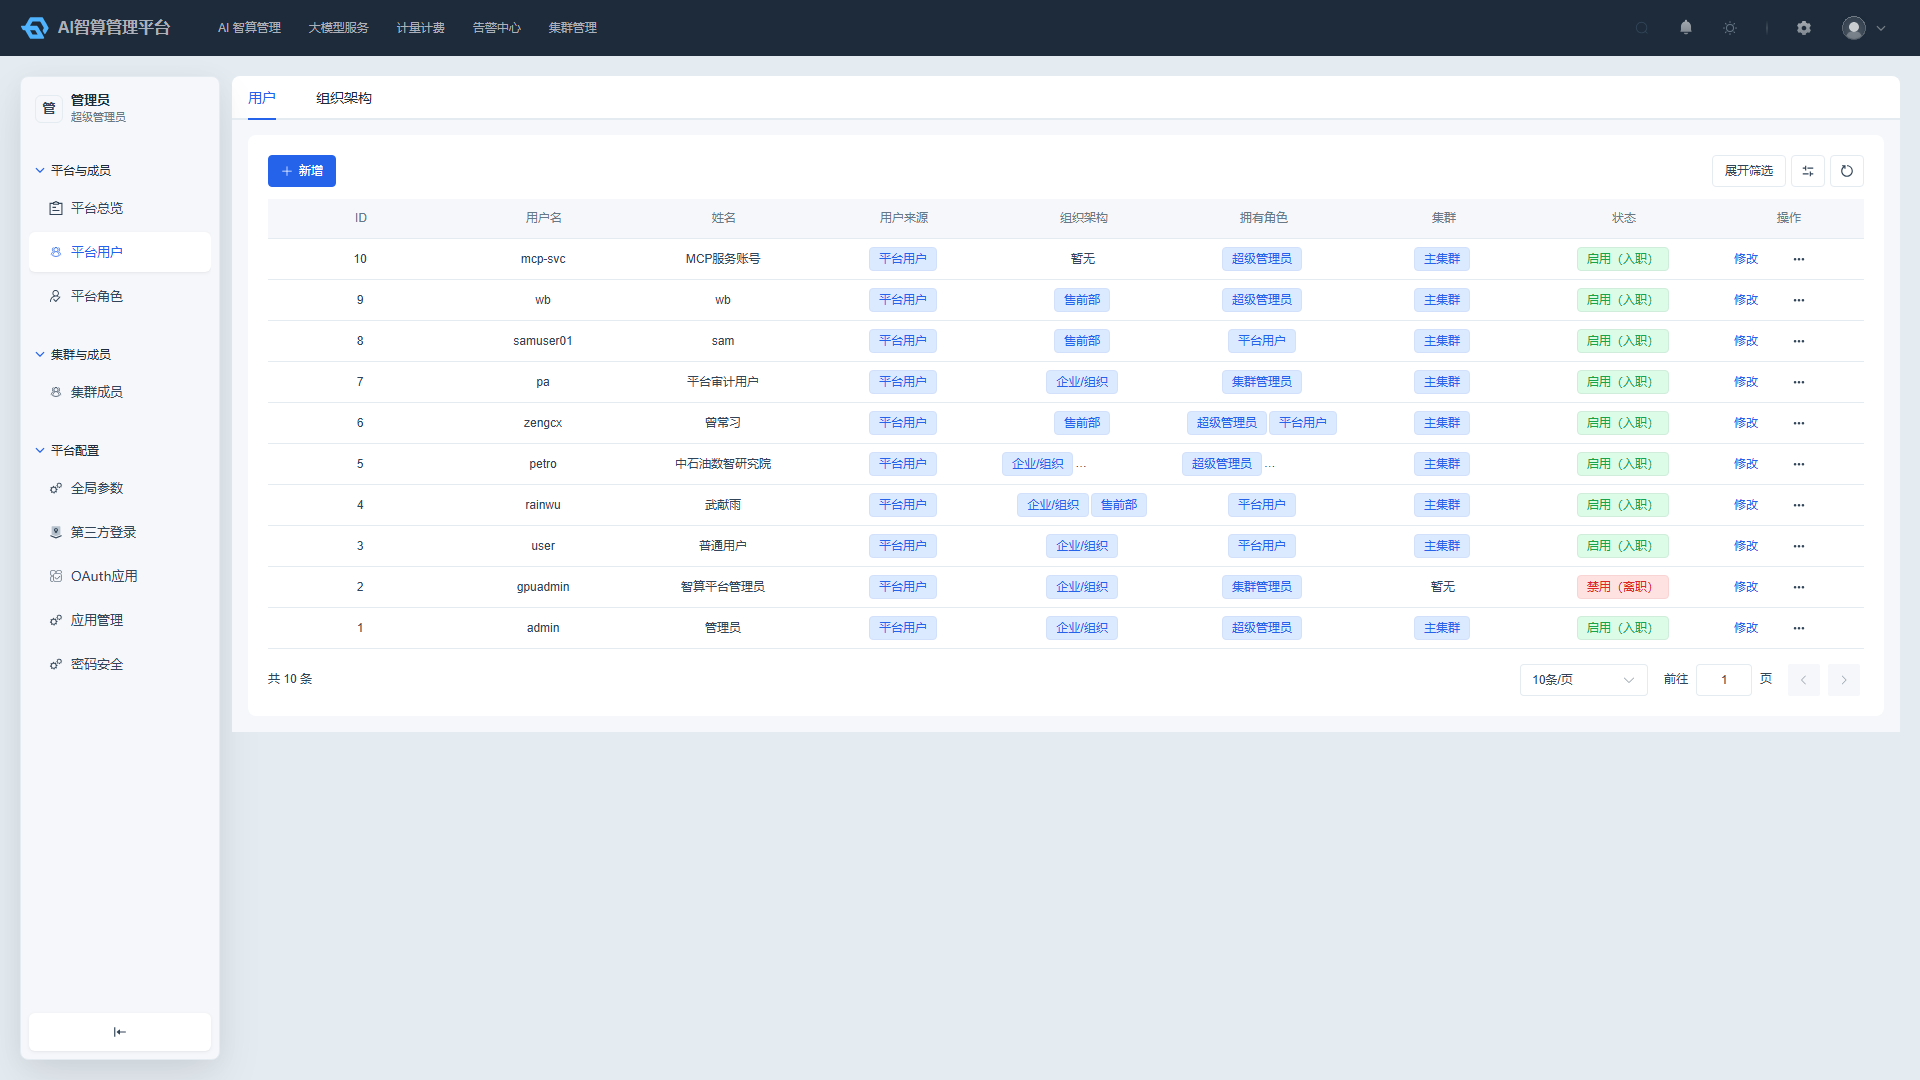
- Switch to the "Organization Structure" tab to view the department hierarchy as a tree table.
- Click the expand/collapse icon in front of a row to view sub-departments.
- Department rows display associated member tags.
Manage Departments
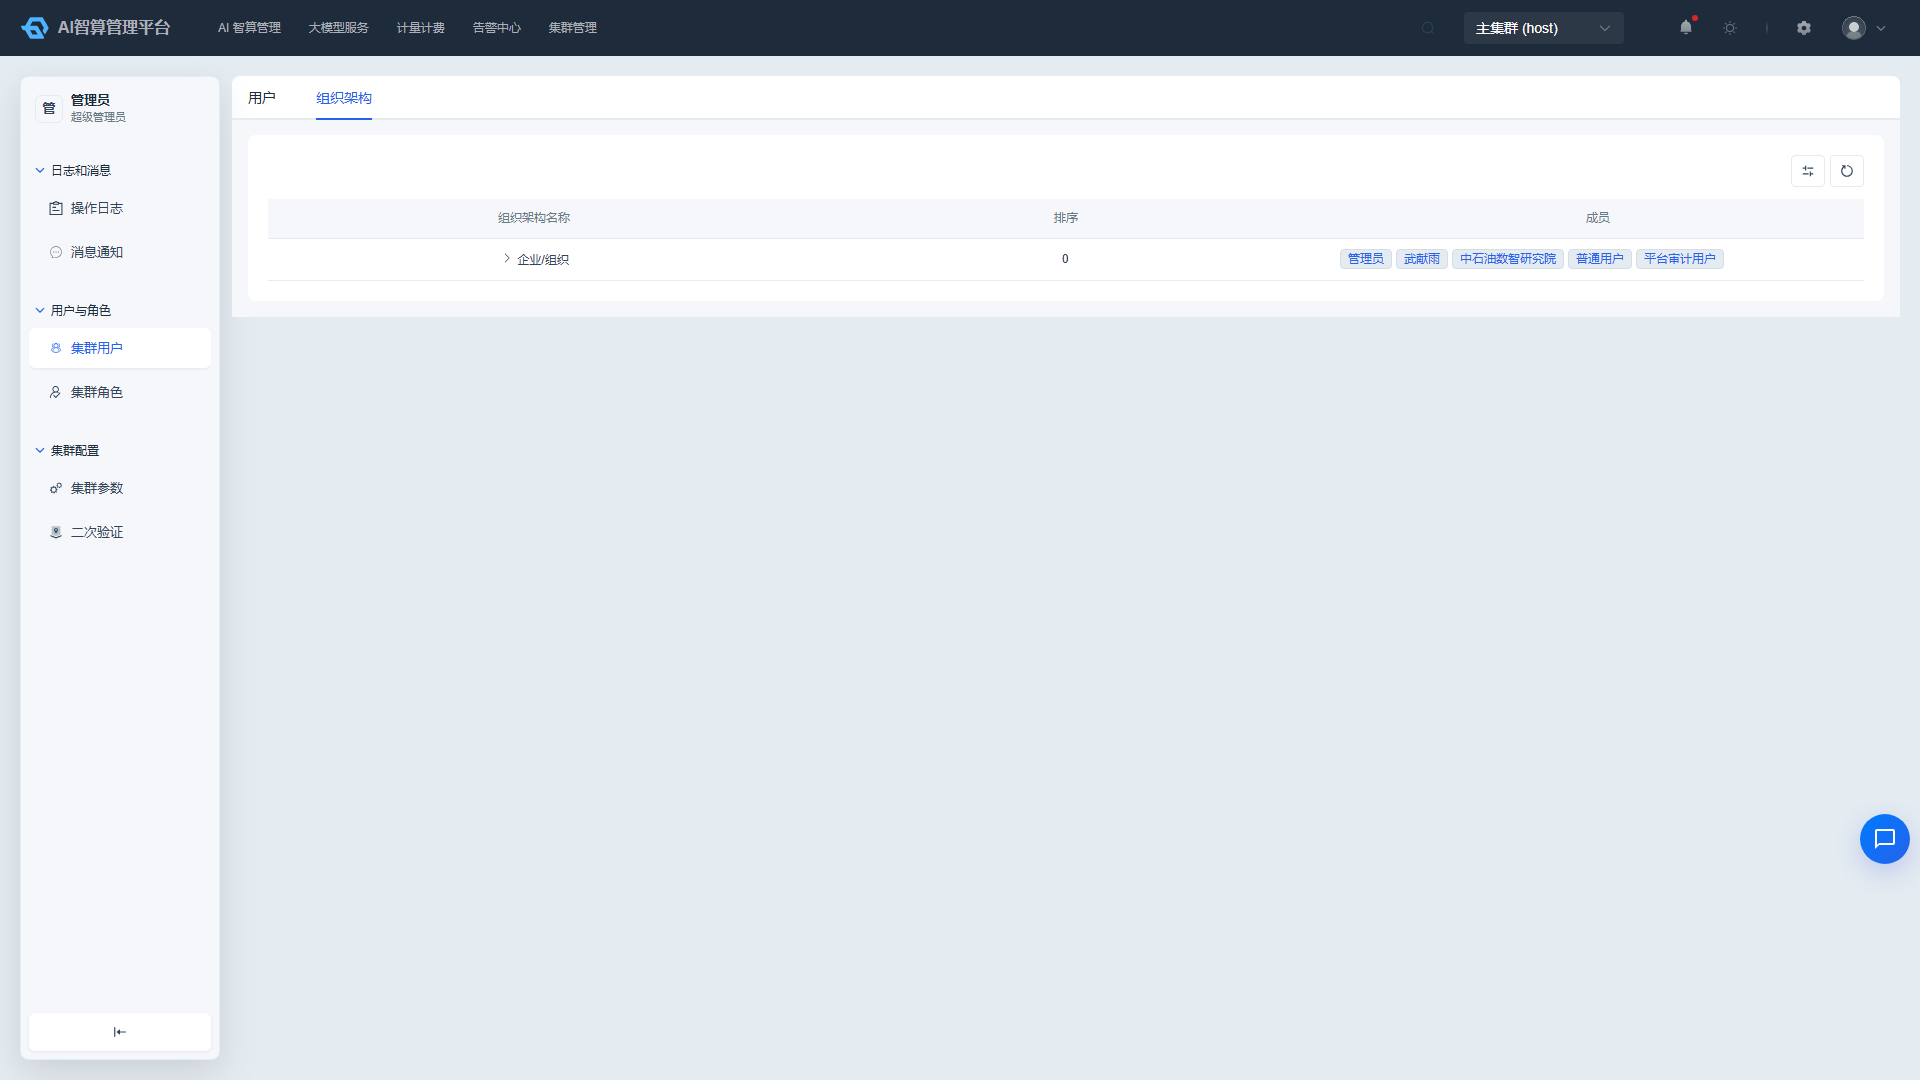
- Click "Add Department" in the "Organization Structure" tab.
- Fill in the department name and select a parent department to create a department node.
- Click "Edit" in the department row to modify department information, or click "Delete" to delete the department (members must be removed first).
- Click "Configure Members" to add or remove member users from the department.
View User List
- Switch to the "User List" tab.
- The list displays: ID, username, full name, user source, organization structure, assigned roles, workspace, project, status (Enabled / Disabled / Pending Activation).
- Use the top filter bar to search by keyword.
Create/Edit User
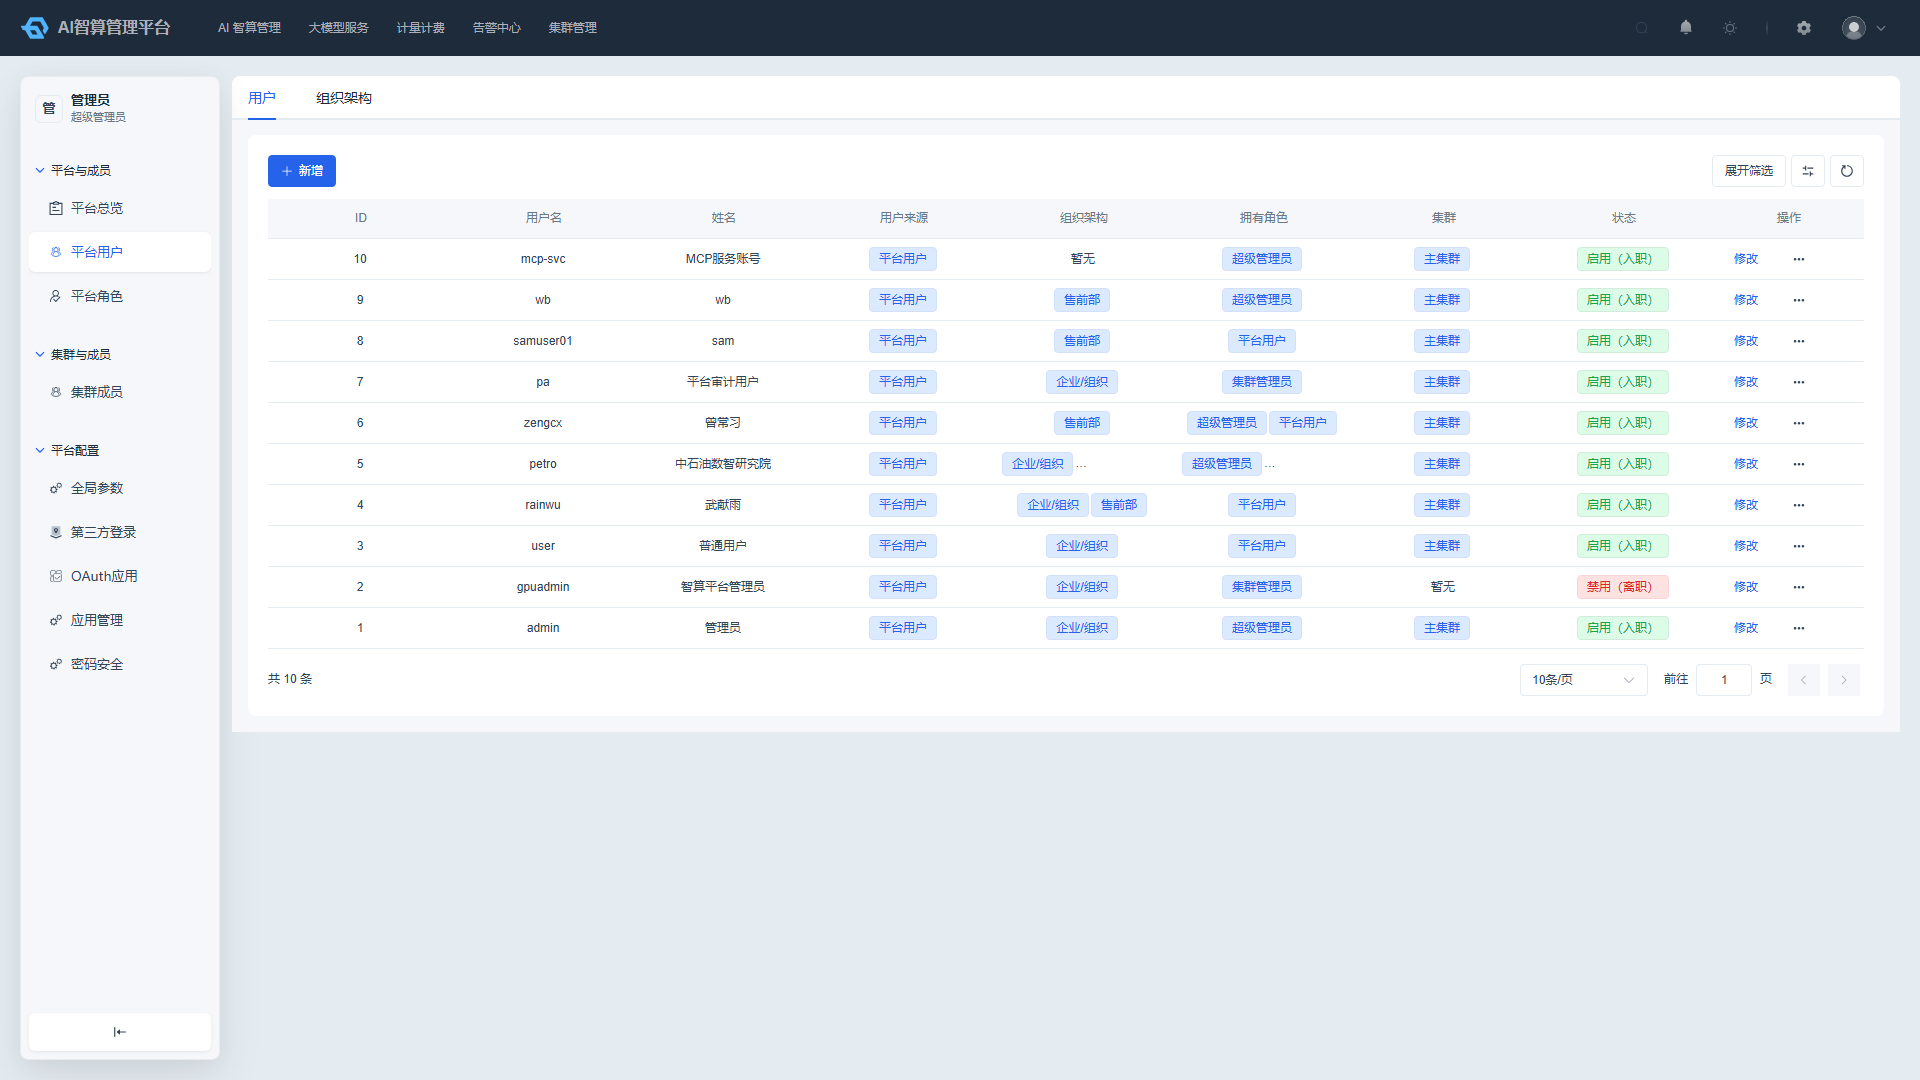
- Click "Add User" and fill in the username, full name, password, department, role, etc.
- Or click "Edit" in a row to modify user information; when editing, you can configure workspace and associated projects.
- Click "Save".
Cluster Roles
View Roles
- Navigate to Cluster Management > Users & Roles > Cluster Roles.
- The list displays: role ID, name (ename), display name (name), role category (Cluster Role / Workspace Role / Project Role).
- Use the top filter bar to search by name and category.
Create Role
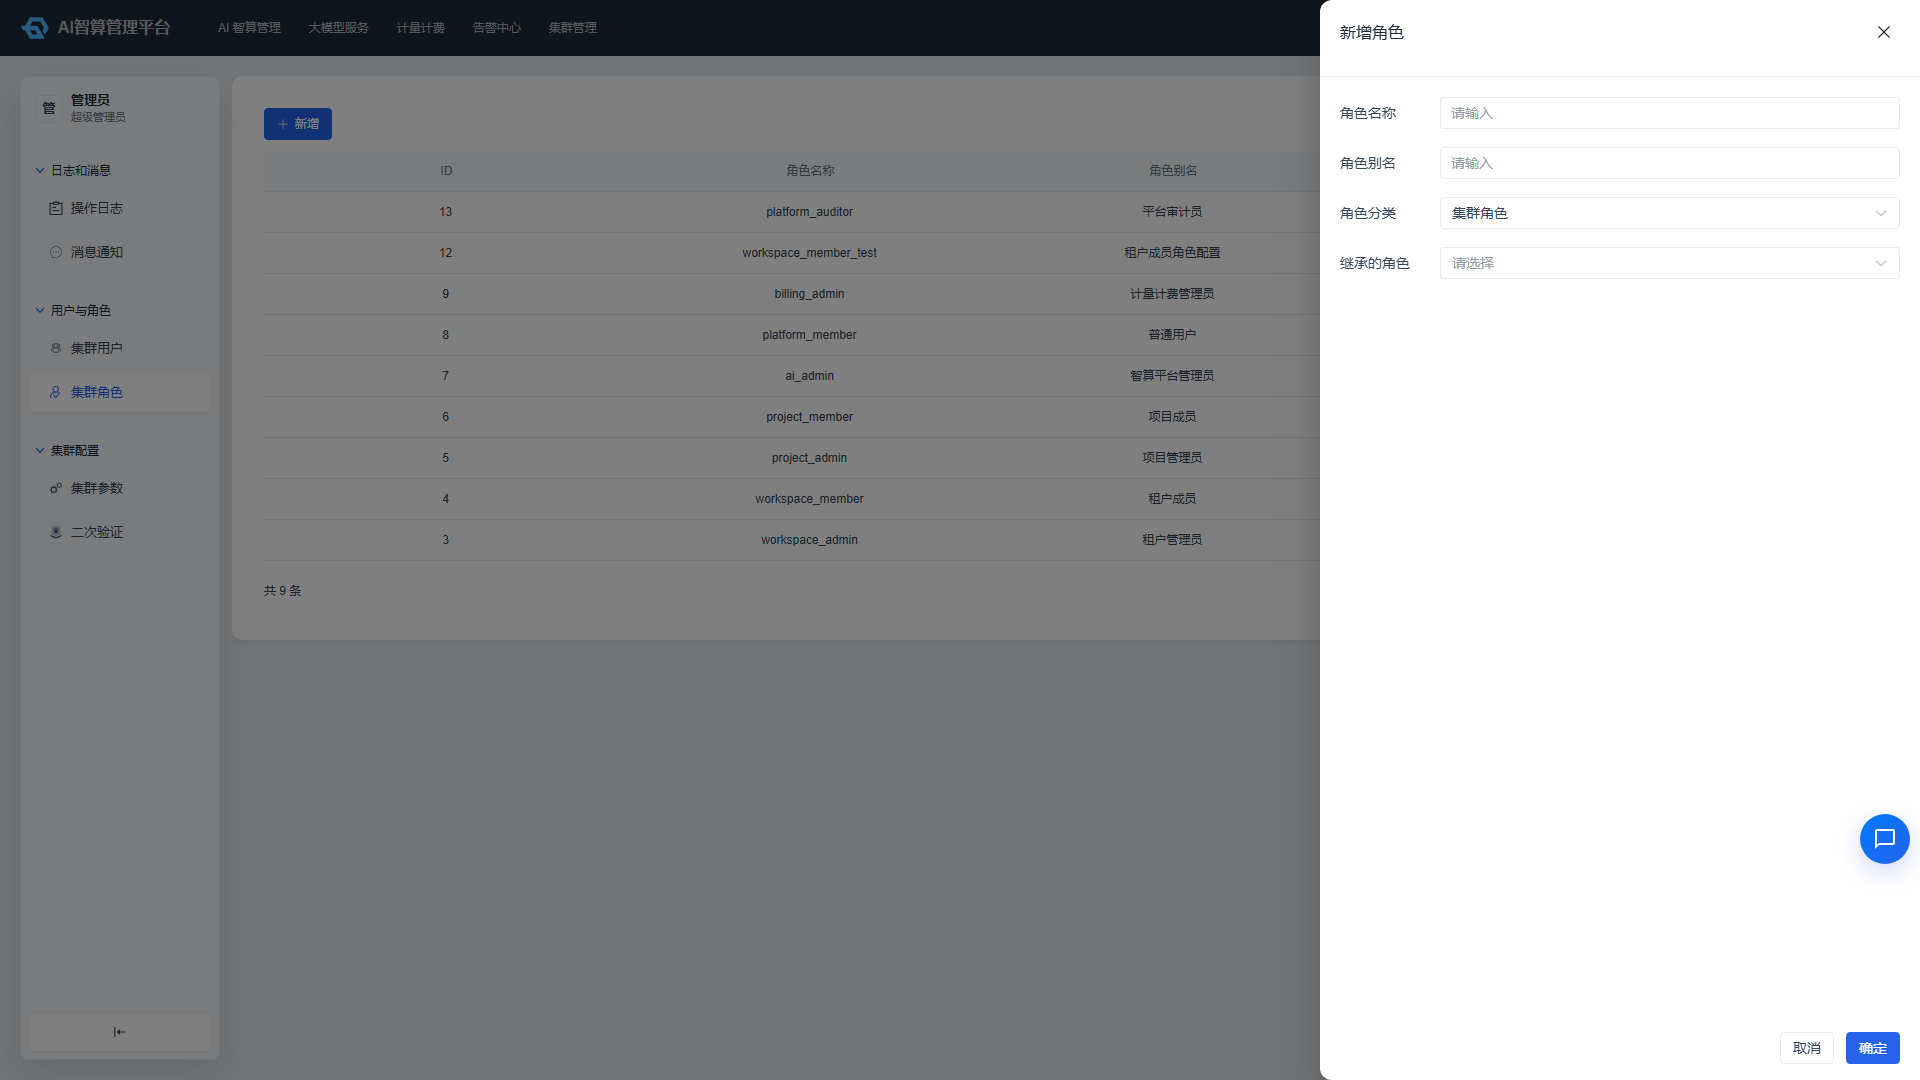
- Click "Add Role".
- Fill in the name (ename), display name (name), and role category; the system checks for duplicates separately and notifies immediately.
- Click "Create".
Configure Permissions
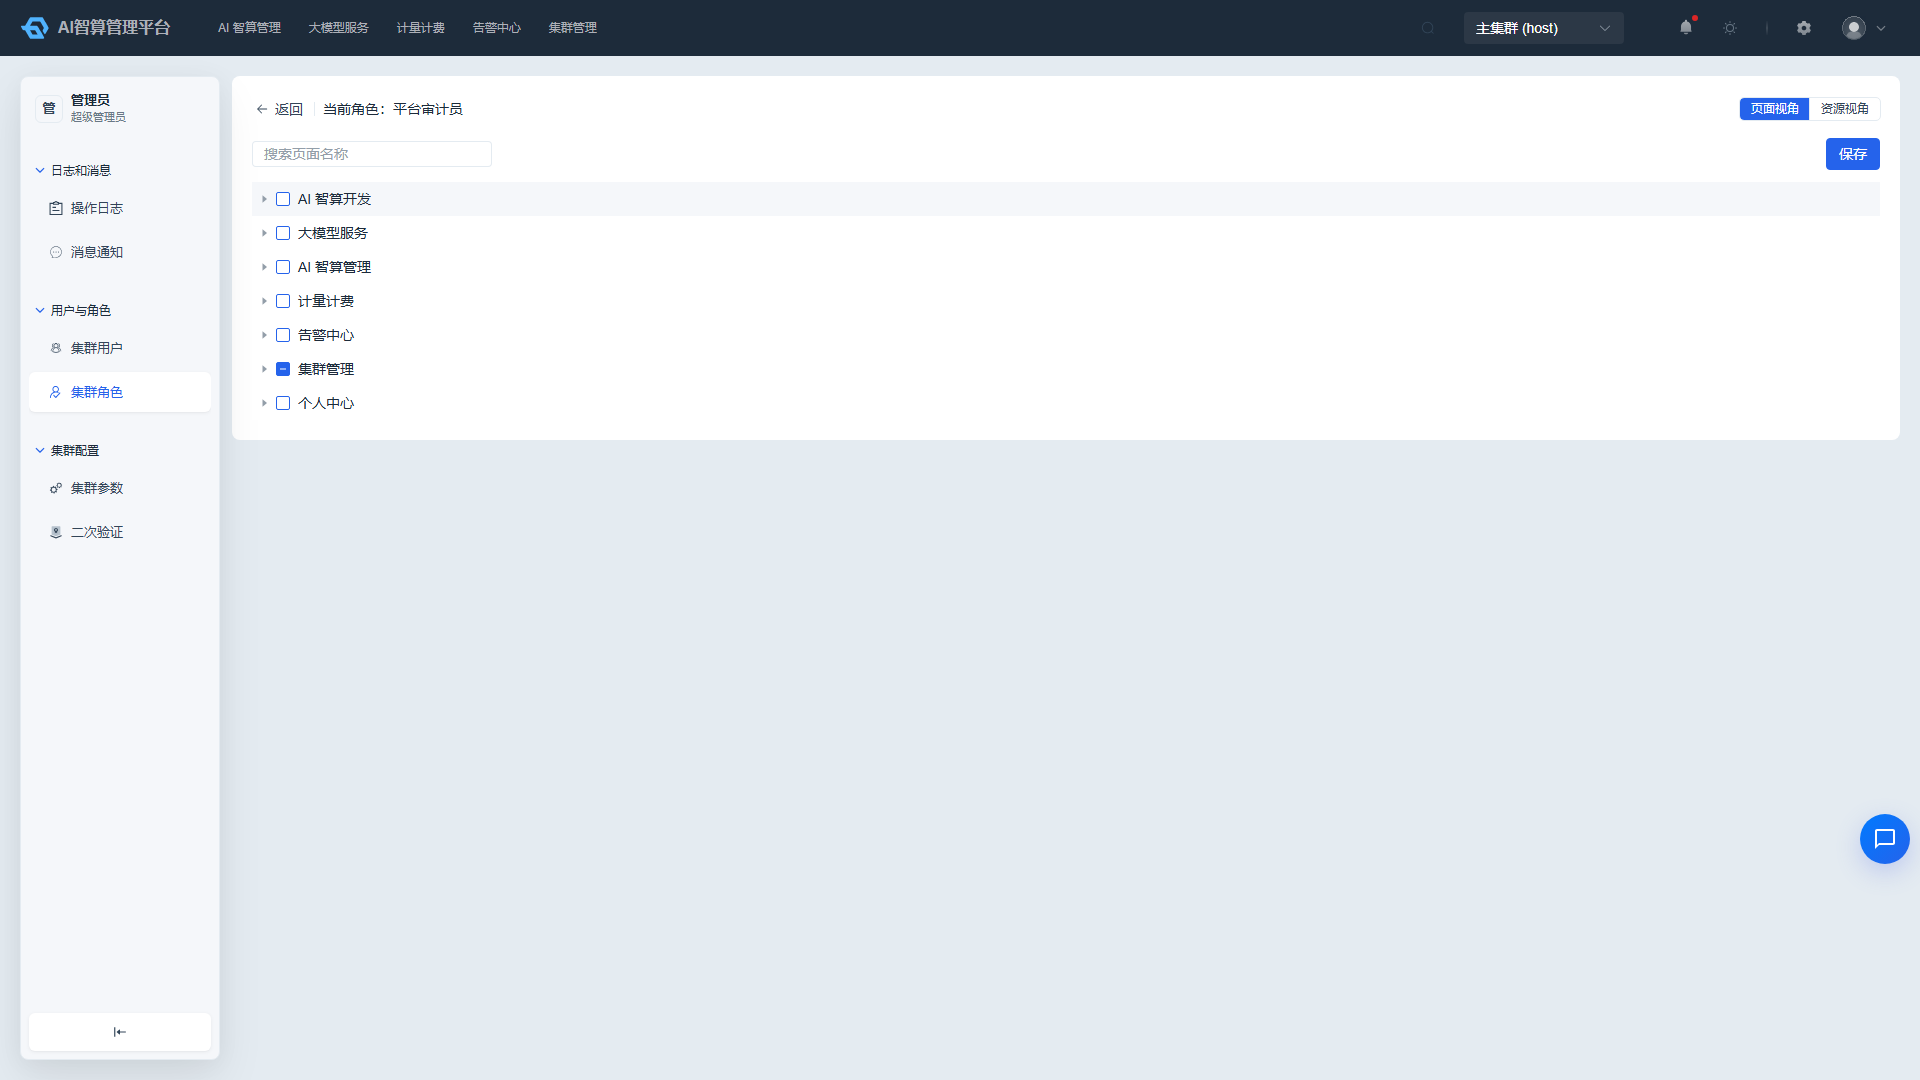
- Click "Configure Permissions" in the role list row.
- Select accessible menus in the menu permission tree.
- Select callable API methods in the API permission tree.
- Select multiple rows and click "Batch Modify Permissions" to quickly set Create / Read / Update / Delete permissions.
- Click "Save".
Manage Plugin Permissions
- Click "Manage Plugins" in the role list row.
- Select the front-end pages accessible by this role.
- Click "Save".
Manage Role Members
- Click "Member Management" in the role list row.
- Add or remove users for this role.
- Click "Confirm".
Clone/Delete Roles
- Clone Role: Quickly create a new role based on an existing role's permissions.
- Delete Role: System-defined roles hide the delete button and cannot be deleted; read-only roles have editing disabled with a notification.
FAQ
Q: What is the difference between cluster users and platform users? A: Platform users are maintained by "Platform Management > Platform & Members" and are platform-level accounts; cluster users are the user view visible within the current cluster, with permissions controlled by cluster roles.
Q: Both the role name and display name show a duplicate error, what should I do? A: Please use a different English name (ename) or display name (name); the system validates uniqueness for each separately.
Q: Why is a certain menu invisible to a role? A: Please check in "Configure Permissions" whether the role has the corresponding menu selected; also check whether the user has been assigned that role.